
Your credentials are already on the dark web.
Check an address now. Then see how StealerHunt matches every leaked record to your domains and tells you who is exposed.
Free, no signup. We'll email you a one-time code to confirm it's your address.
What you see once you are in
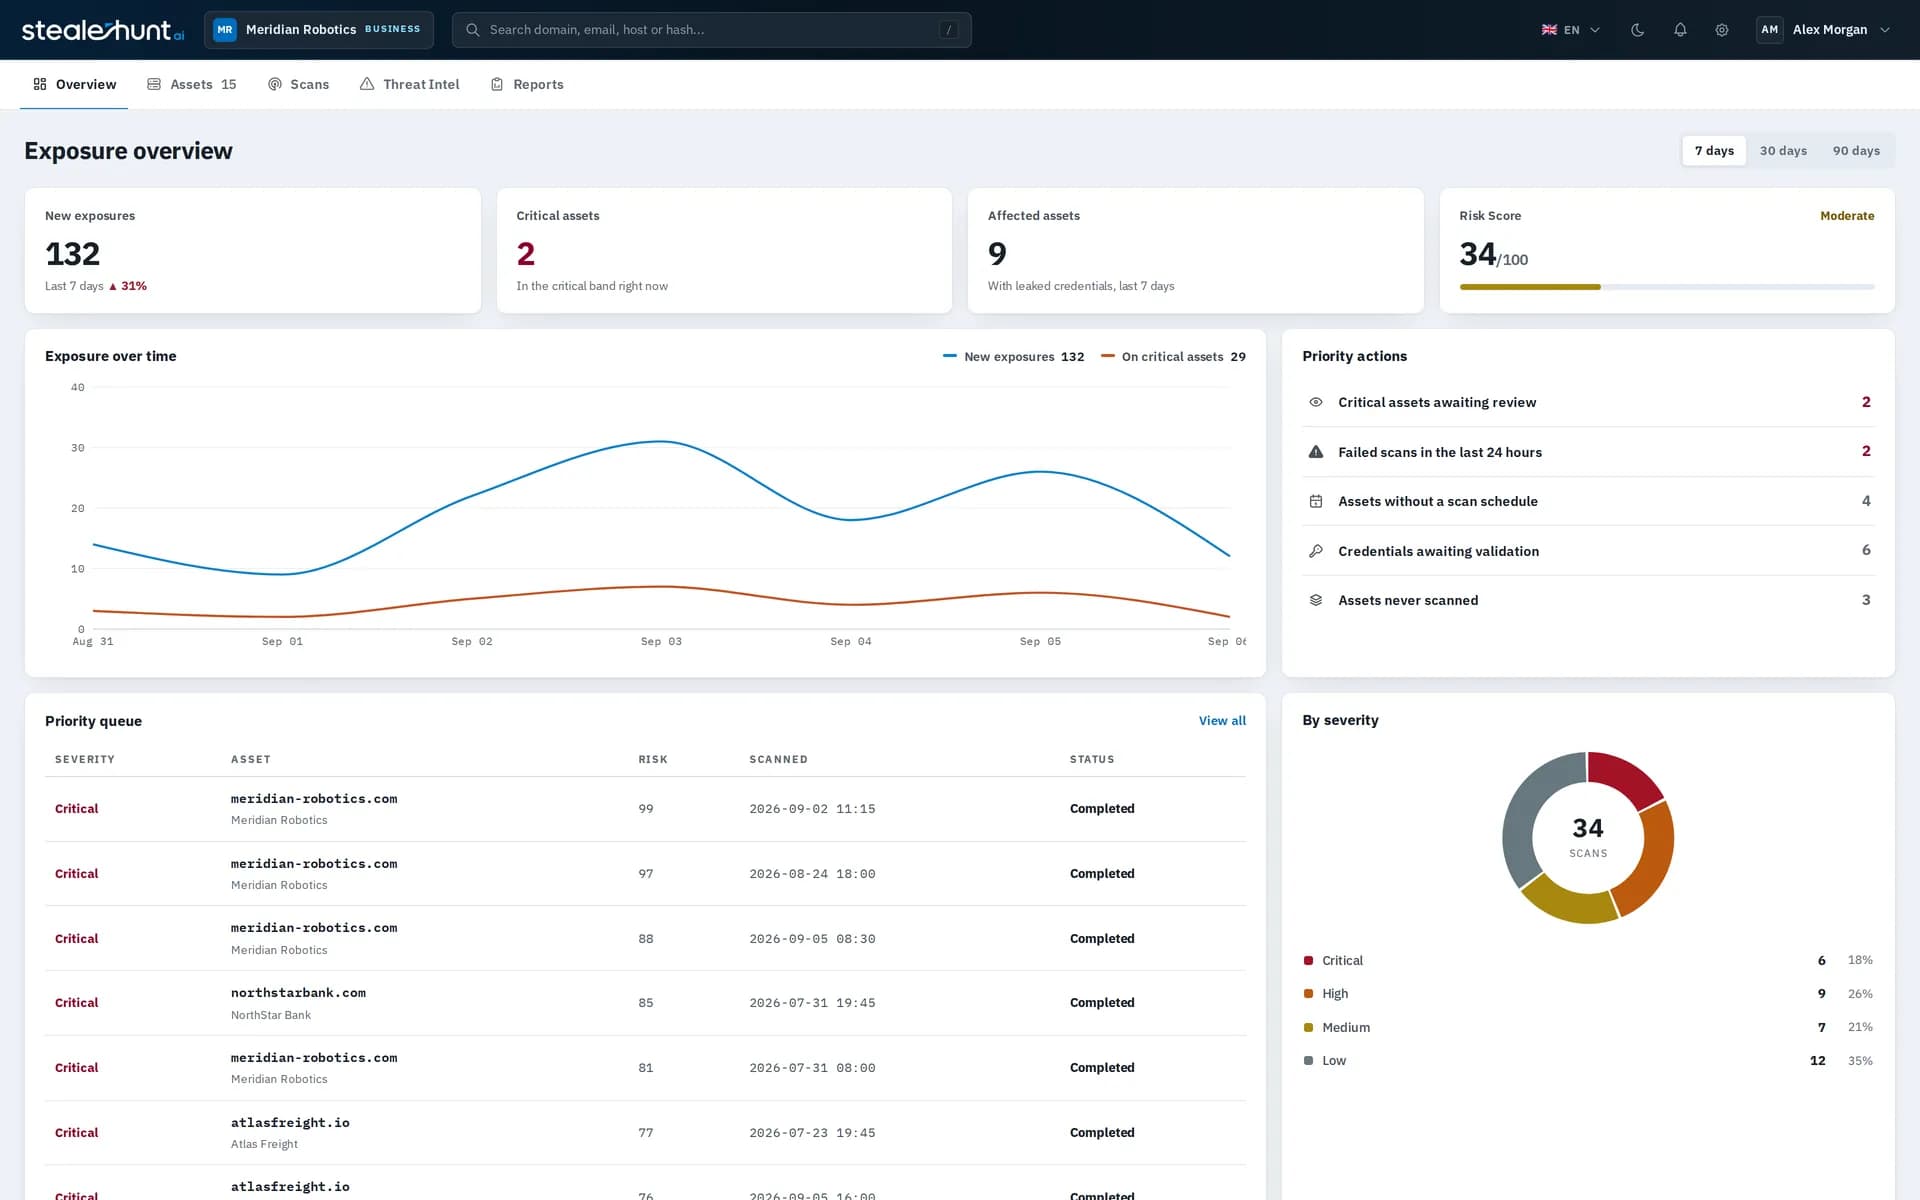
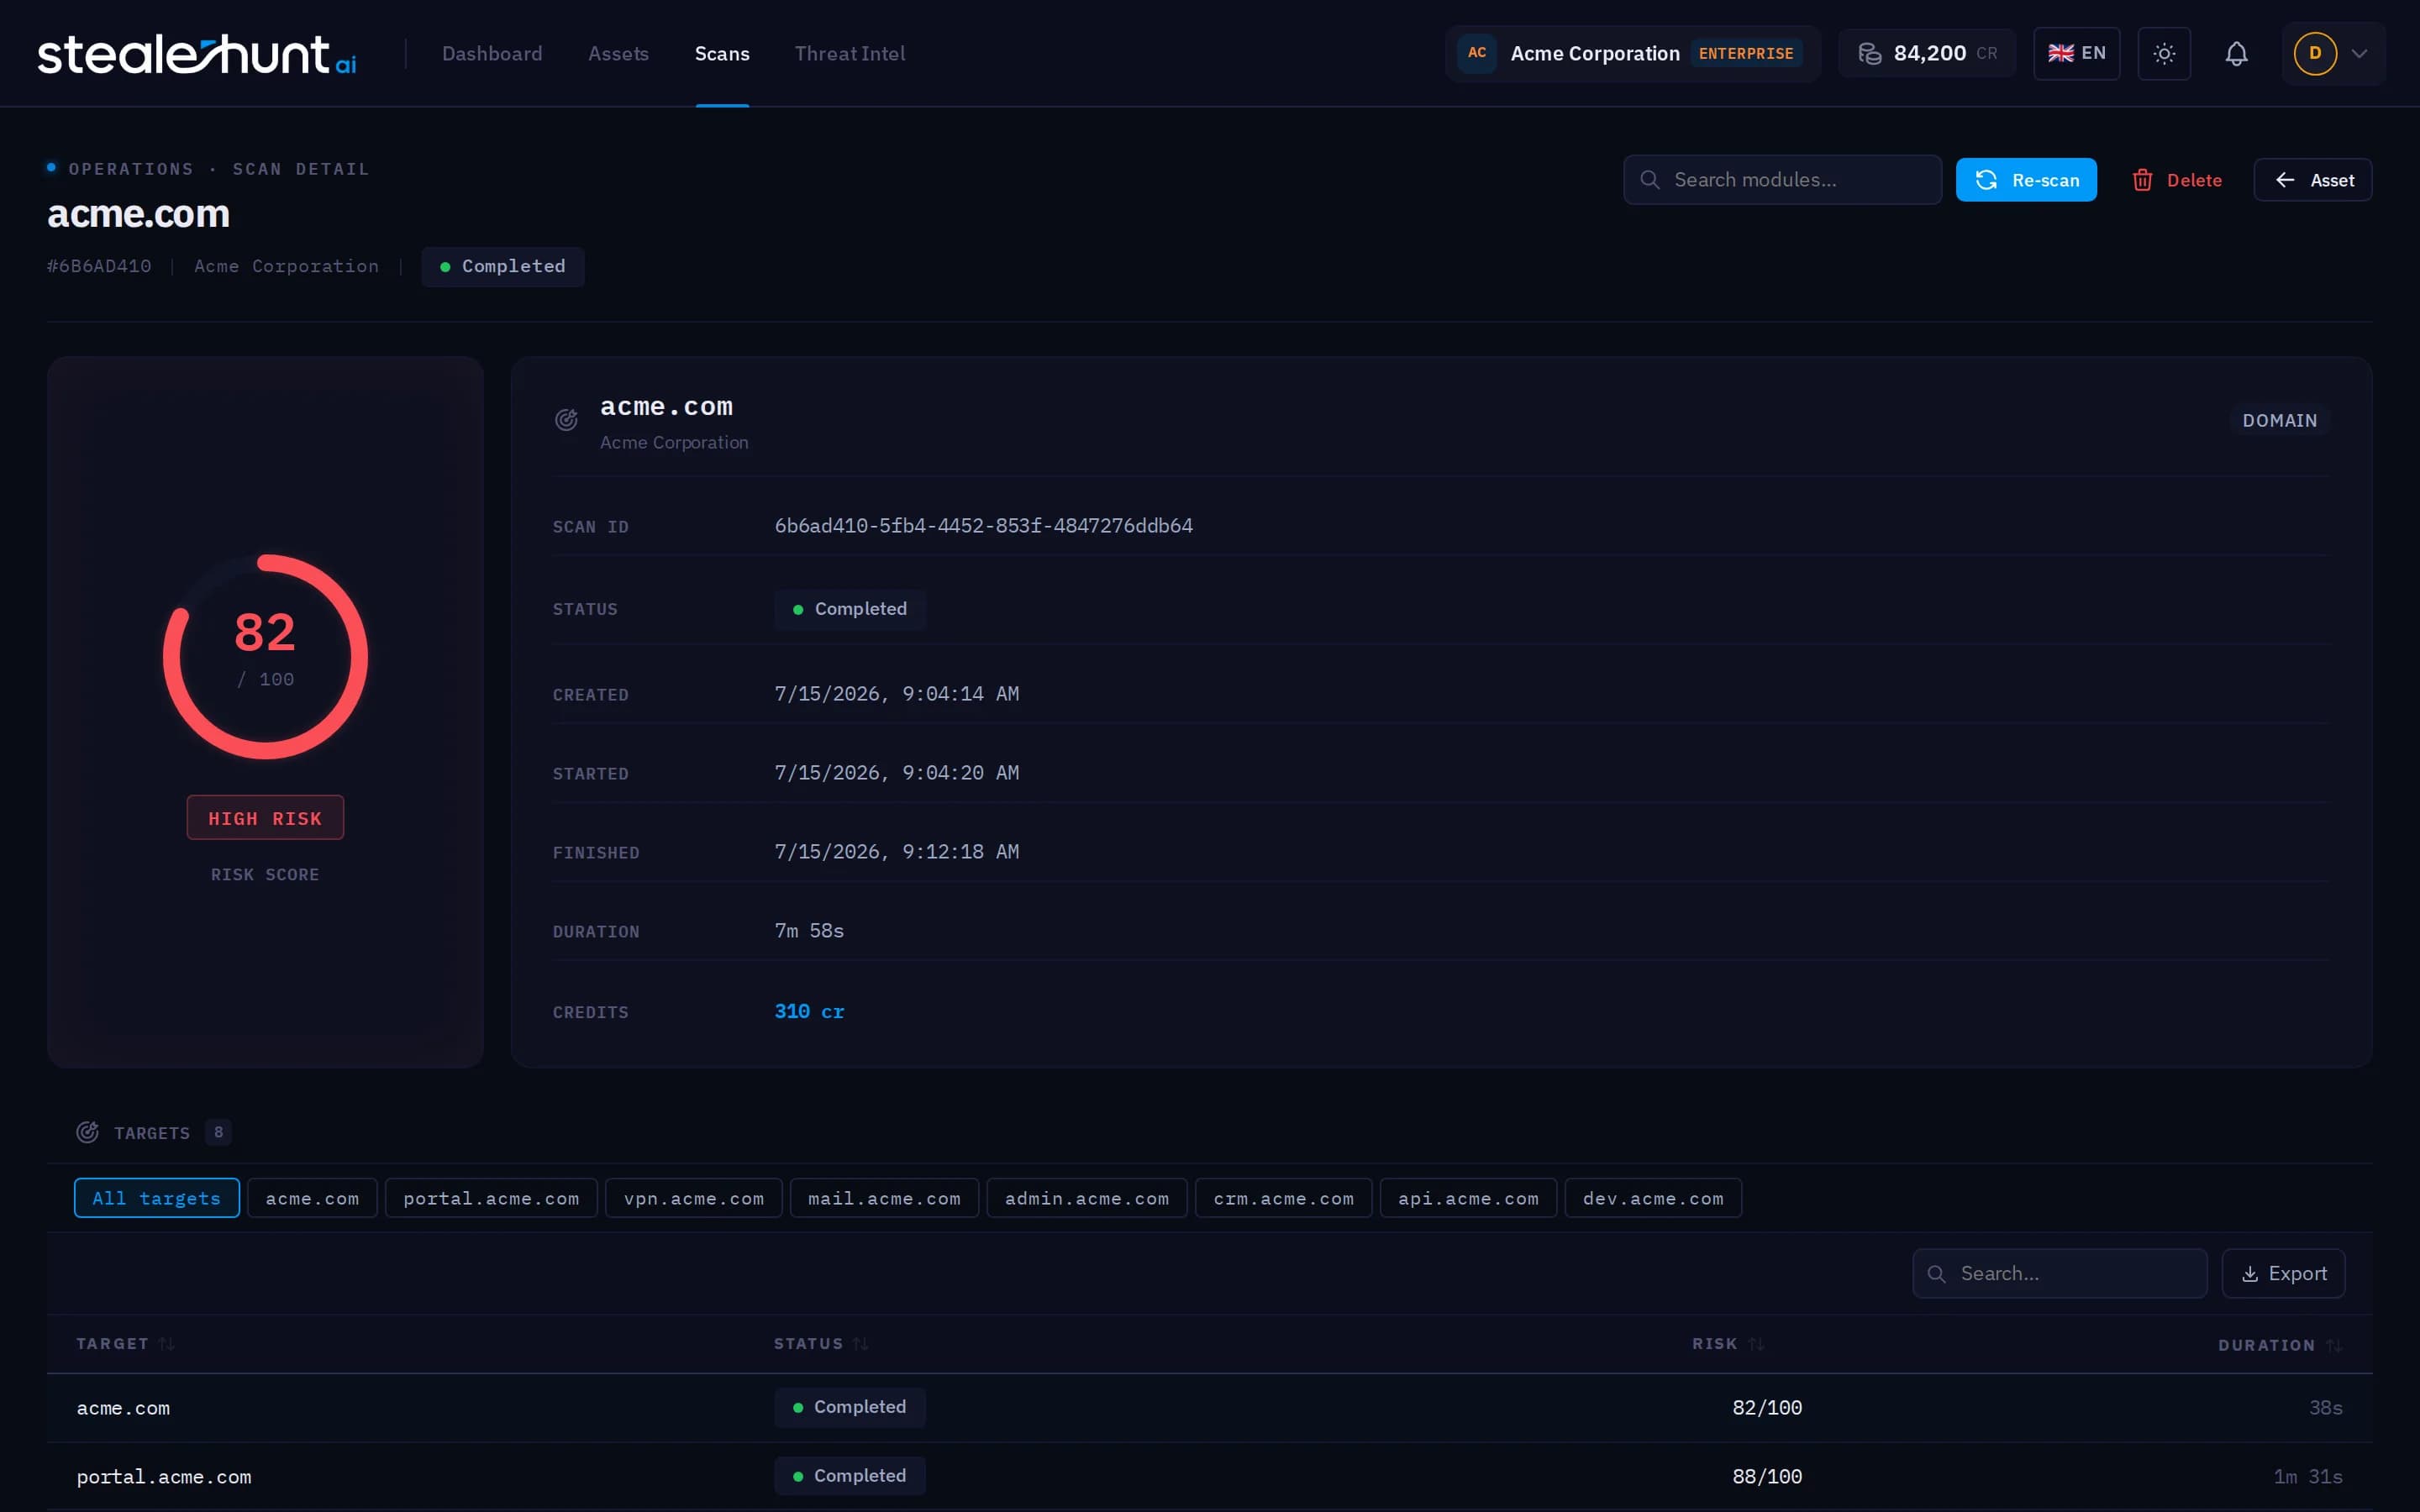
One console for the whole organization: exposure by asset, every finding with its evidence, and a risk score after each scan.
- Exposure by asset
- Which domains and subdomains leak most, trended over the last 30 days.
- Findings with evidence
- Masked credentials, source and first-seen date on every record, ready for triage.
- A risk score after every scan
- Per-asset scoring with timing and cost in the open, exportable in one click.
How a stealer log becomes a closed finding
Collection, matching and classification run as one pipeline. Nothing reaches your analysts unless it belongs to your organization.
- 1
Stealer data
Stealer logs, combolists, breach databases and ransomware leak sites are ingested and parsed as they surface.
2026-05-11 03:41:22 | lumma | m***@finance-corp.com : ******** | vpn.finance-corp.com - 2
Matched to your assets
Every record is cross-referenced against the domains and subdomains you register. Noise never reaches your queue.
match finance-corp.com asset vpn.finance-corp.com - 3
Classified and delivered
Each finding resolves to employee, third-party or customer, is risk-ordered, and lands in triage, your SIEM or a board-ready PDF.
class Employee priority P1 status new
One problem, covered end to end
Most CTI suites treat credential leaks as one module among a dozen. StealerHunt does a single thing and owns every step of it.
- KVKK and GDPR aligned
- Masked evidence by default
- Tenant isolation per organization
- Security review on every release
No reseller feed in the middle
Parsing, deduplication, identity classification and triage are ours, from raw stealer log to closed finding.
The POC runs on your own domains
No sandbox tenant, no sample dataset. You get what is already exposed, masked and written for the meeting afterwards.
Built around the analyst’s day
Per-finding triage states, suppression rules that survive re-scans, org-scoped access for MSSPs, and a REST API into your SIEM.
See your organization's real exposure
The POC runs on your own domains and your own leaked data: masked, sanitized and ready to brief.